How to Access AxiumTech.net with the Correct HTTPS Address begins with one simple check: confirm the browser shows https://axiumtech.net and a padlock. This short guide explains why that padlock matters, how to inspect the site identity quickly, and what to do when common HTTPS warnings appear. It targets readers who want a step-by-step, low-friction path to reach AxiumTech.net safely on desktop and mobile without guessing or exposing credentials.
Key Takeaways
- Always access AxiumTech.net using the exact HTTPS address https://axiumtech.net to ensure a secure connection.
- Verify the padlock icon and inspect the SSL/TLS certificate details to confirm the site’s identity and certificate validity before submitting sensitive information.
- On desktop browsers, manually type the URL or use trusted bookmarks to avoid phishing from deceptive links.
- Mobile users should use updated browsers and cross-check certificates when details appear incomplete, leveraging password managers for added security.
- If HTTPS errors like certificate mismatch, expiry, or redirect loops occur, do not bypass warnings; instead, identify the error and report it to site support.
- Site administrators should implement proper SSL/TLS certificates and consistent 301 redirects to maintain secure and accessible HTTPS connections.
What Is AxiumTech.net And Why HTTPS Matters
Fact first: AxiumTech.net is a live technology and news site reachable at the HTTPS address, and HTTPS protects visitors by encrypting data and verifying identity.
AxiumTech.net publishes tech news, health coverage, and practical guides. When users log in, subscribe, or send form data, HTTPS prevents eavesdroppers from intercepting that information. Beyond privacy, the SSL/TLS certificate confirms the site’s domain and reduces the chance of phishing with lookalike domains.
A clear example: a researcher attempted to log into a news comment account over HTTP in 2024 and had credentials captured by a network sniffer. With HTTPS, that same traffic would have been encrypted. For AxiumTech.net, this means editorial content and any user accounts are safer when the certificate is valid and the address reads https://axiumtech.net.
Practical warning: a padlock alone is not an automatic endorsement, users should still verify certificate details for domain match and expiry before entering sensitive data.
How To Verify The Correct HTTPS Address Before You Click
Answer up front: always confirm the exact address and certificate basics before following links to AxiumTech.net.
Start by pausing before you click. Look at the visible link text and the surrounding context. If the link is embedded in email or social media, hover (desktop) or press-and-hold (mobile) to preview the destination. Confirm the domain ends in “axiumtech.net” and not a similar but fraudulent name.
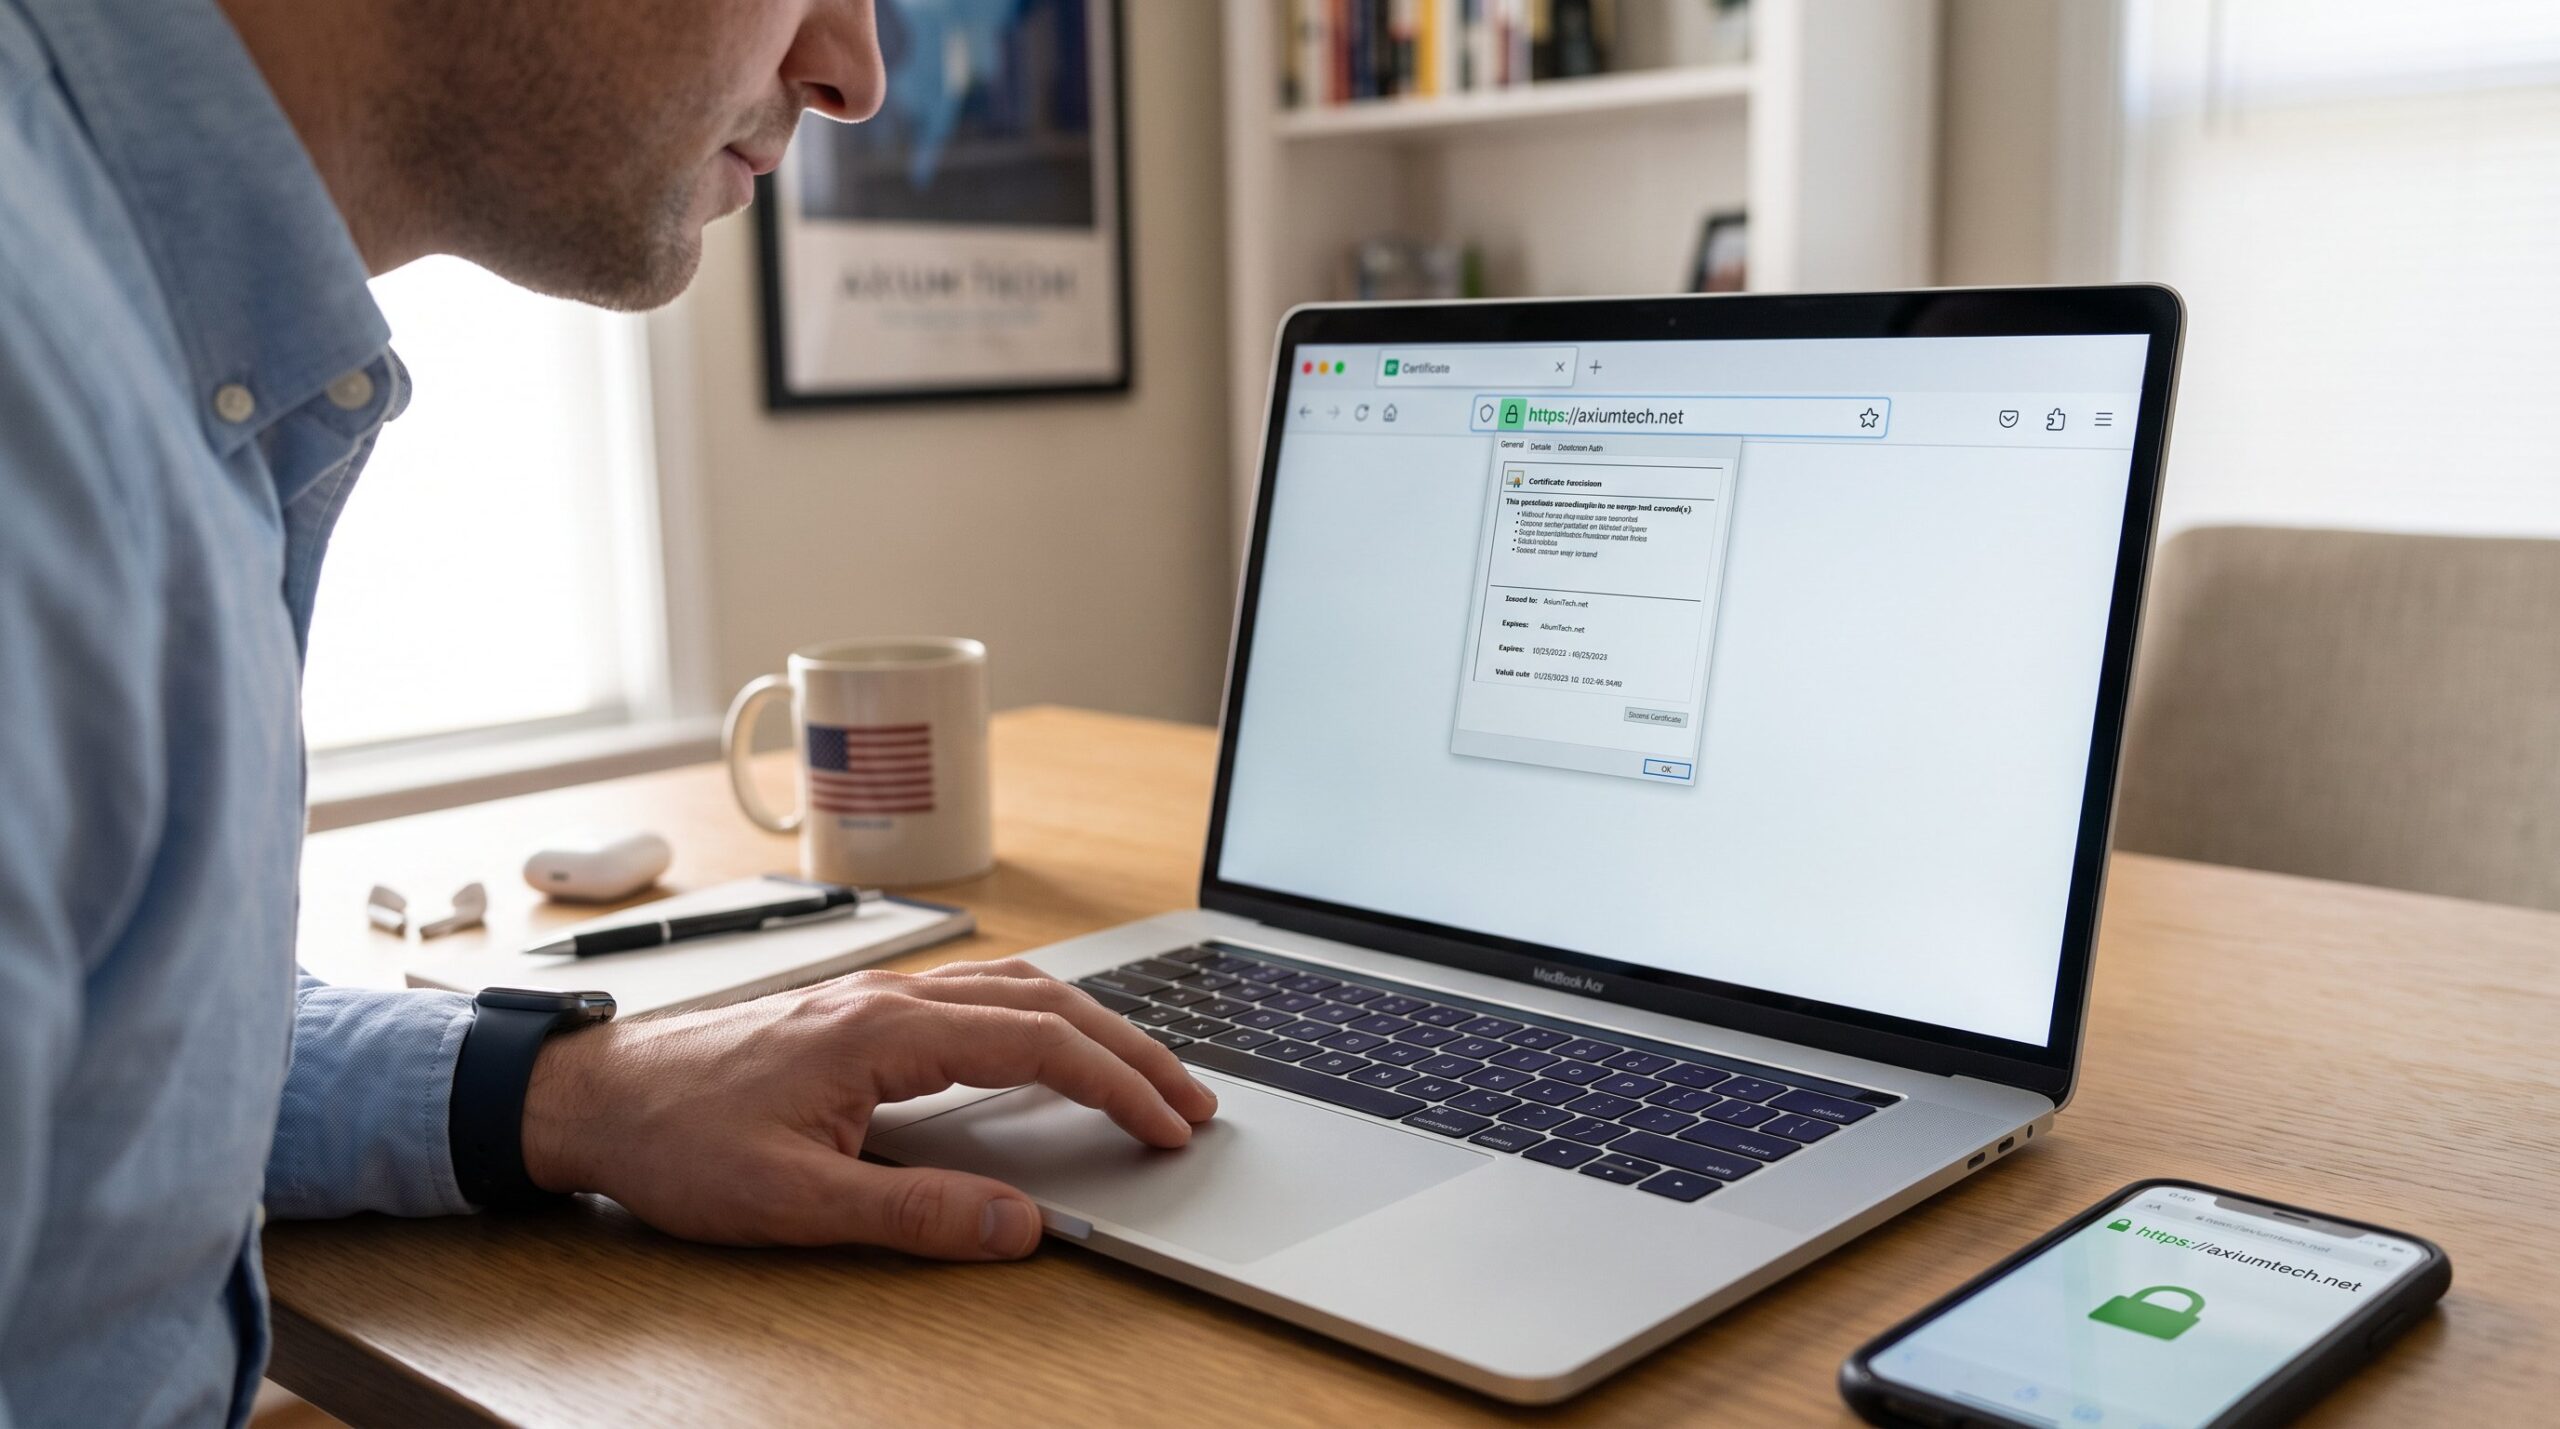
Next, check the address bar after the page loads: it should read https://axiumtech.net and show a padlock. If the domain differs, close the tab.
A practical verification step that helps many readers: compare the link against a trusted bookmark or type https://axiumtech.net manually. Manual entry removes uncertainty introduced by redirects or deceptive anchors.
This guide uses tips adapted from established advice on spotting fraudulent sites: for a concise primer on visual checks and certificate inspection, fraud detection tips.
Checking Certificate Details And Site Identity (Quick Steps)
Direct answer: click the padlock, inspect the certificate owner, domain names, issuer, and expiry.
Quick steps (desktop):
- Click the padlock icon left of the address bar.
- Open “Certificate” or “Connection is secure” details.
- Confirm the certificate lists axiumtech.net (and www.axiumtech.net if used).
- Check the issuer is a recognized CA and the expiry date is in the future.
Quick steps (mobile):
- Tap the padlock or site info icon.
- View certificate basics (some mobile browsers show only limited details).
- If details are missing, prefer typing the URL manually or using a saved bookmark.
Real-world tip: certificates sometimes cover both the naked domain and www via Subject Alternative Names (SAN). If a certificate lists axiumtech.net in SAN, the match is valid. If mismatch or expiry appears, do not submit credentials: instead, report the issue to site support.
Step-By-Step: Accessing AxiumTech.net Securely On Desktop Browsers
Key point first: on desktop, type the address and inspect the padlock before interacting with the page.
- Open a current browser (Chrome, Firefox, Edge, Safari). Keep it updated to avoid known bugs.
- In the address bar, type exactly: https://axiumtech.net and press Enter. Typing removes redirect ambiguity.
- Wait for the page to fully load. Look for the padlock and make sure the browser does not show warnings like “Not secure.”
- Click the padlock to view certificate basics. Verify the domain and expiry.
- If planning repeated visits, save a bookmark labeled “AxiumTech, Secure” for quick, verified access.
Additions for administrators: if an internal redirect or CDN is in place, ensure the server returns proper 301 rules from HTTP to HTTPS and that the certificate is installed at the origin and edge. For readers wanting more context about AxiumTech’s content and site structure, the site’s overview explains its tech coverage and categories in detail via a short guide on the network’s topics at site overview.
Practical caution: do not bypass browser warnings by proceeding to advanced options unless a trusted admin confirms the certificate issue.
Step-By-Step: Accessing AxiumTech.net Securely On Mobile Devices
Fact first: mobile browsers show limited certificate details, so extra care is needed when using phones or tablets.
- Use an up-to-date Chrome, Safari, or Firefox app. Older mobile browsers may not surface certificate problems.
- Type https://axiumtech.net or open a trusted bookmark saved earlier.
- After the page loads, tap the padlock or site info. If the browser exposes certificate details, verify the domain and expiry.
- If details are truncated or unavailable, confirm the link by checking a desktop or a trusted bookmark before submitting credentials.
Example: a user on a shared café Wi‑Fi tapped a shortened social link and landed on an impersonator domain. Because the mobile browser showed a padlock but lacked certificate details, the user cross-checked the bookmark on a laptop and avoided exposing a password.
For frequent mobile readers, enable automatic updates and use a password manager: password managers often detect domain mismatches and refuse to fill credentials on incorrect hosts. For additional reading on finding the latest posts and staying on official content feeds, consult the helpful guide on locating recent updates with verified links at latest posts tips.
Troubleshooting Common HTTPS Errors When Visiting AxiumTech.net
Immediate answer: identify the error code, do not ignore warnings, and follow targeted fixes for the specific error.
Common errors and what they mean:
- Certificate mismatch (ERR_CERT_COMMON_NAME_INVALID): the certificate’s domain does not match axiumtech.net. This often happens after misconfigured redirects or when a certificate is issued for a different hostname.
- Expired certificate (ERR_CERT_DATE_INVALID): the certificate reached its expiry date and needs renewal.
- Mixed content warnings: some resources (images, scripts) still load over HTTP, reducing overall security.
- Redirect loops (ERR_TOO_MANY_REDIRECTS): conflicting server, CDN, or application redirect rules cause endless HTTP↔HTTPS bouncing.
Detecting the root cause: capture the browser error code and review the certificate details. If on a managed network, temporarily test from a home or cellular network to rule out proxy interference.
Follow-up resources in this site cluster explain privacy and terms you might inspect when support is needed: check the site’s privacy review page for contact channels and support instructions at privacy details.
Fixes For Certificate Mismatch, Mixed Content, And Redirect Loops
Headline fix: apply the targeted solution for each error rather than a blanket workaround.
Certificate mismatch fixes:
- For site owners: reissue the SSL/TLS certificate to include axiumtech.net and www.axiumtech.net in the SANs: then install and test on origin and CDN.
- For visitors: do not proceed: notify site support and try accessing the bookmarked URL.
Expired certificate fixes:
- Site admins must renew with the CA and deploy the new cert. Visitors can retry after a short wait.
Mixed content fixes:
- Replace internal http:// resource links with https:// and use protocol-relative URLs only when necessary. Run a crawler to list remaining HTTP resources.
Redirect loop fixes:
- Inspect server and CDN redirect rules for double rewrites (for example, both server and CDN forcing different redirects). Normalize to a single HTTP→HTTPS 301 rule.
Practical warning and lesson learned: a site operator once layered a redirect at the web server and another at the CDN: the result was a 302 loop that prevented all users from reaching content for three hours. Simpler rules and a staging test would have avoided the outage.
For administrators troubleshooting remote access or configuration implications, the site’s technical guide on remote setups offers configuration tips that align with secure access patterns at remote access guide.
Conclusion
Final insight: the fastest, safest way to reach AxiumTech.net is to type https://axiumtech.net, check the padlock, and inspect certificate basics before entering credentials. If errors appear, identify the specific code, avoid bypassing warnings, and report problems through the site’s support channels. For readers who want a deeper tour of AxiumTech’s content and structure, a short internal overview explains the site’s coverage and navigation in practical terms at site overview.